About
How I got here
Hands-on network and cloud security, on top of six years of technical operations and project management. For most of those years I was the one person every account, credential, client and supplier ran through; lately I've been securing infrastructure on purpose, not just keeping it running.
This year I finished the Cloud Network Defender programme (CND 53) at Bar-Ilan's School of Hi-Tech and Cyber Security: Windows Server and Active Directory, Cisco, Check Point, Palo Alto Networks, Linux, AWS. The final project was four AWS accounts behind an on-premises Palo Alto firewall: users pushed in from Entra ID over SCIM with no AWS passwords, least-privilege permission sets, service control policies, Fargate in private subnets with no NAT gateway in its path, a second region built and failed over for real, and every route hairpinned through the firewall for App-ID policy, decryption and logging. 97 documented steps. The write-up is under Projects.
Before that, at XP.NETWORK, I ran the AWS staging and production environments for an NFT bridge across 30+ blockchains: S3, CloudFront, TLS, Cloudflare DNS and redirects, registrar and nameserver migrations. Every account the company owned went through me - AWS, MongoDB, Heroku, GitHub, Google Workspace, every social platform - opened with minimum access and the 2FA kept on a separate phone. Security came before the certificates. In 2020 I was taking vulnerability findings on live WordPress sites to the companies that owned them: choosing who to approach, making contact cold, presenting to digital managers and executives, and working through those companies' own web suppliers until the issues were actually closed. Most of them acted like they didn't want the help. The issues got fixed anyway.
The bigger job at XP.NETWORK was everything around the infrastructure. I wrote the weekly investor update for four years, helped raise close to $6M, saw 19 blockchain grants through to final payment, and built and ran a 24/7 community team across six countries. When the company wound down, I designed the seven-year legal retention archive across three jurisdictions and 60+ investors, the kind of work that has to be right the first time, because once the company is gone there is nobody left to correct it.
Since early 2025 I've also been setting up Blumberger Law Firm's technology from zero: domains, Cloudflare, website security, Microsoft 365 security, client records, financial accounts, supplier negotiations. Different industry, same position: everything technical the firm runs on is mine to design and mine to answer for.
My standard hasn't changed across any of it: not whether something looks right in a diagram, but whether it holds up when someone's actually using it.
Next: the AWS Solutions Architect Associate exam, going deeper on firewalls and cloud security, and AI tooling along the way. Everything technical I know, I learned because a build in front of me needed it. That is still how I choose what to learn next.
About this site: the app is the one the project deployed on ECS Fargate. The AWS environment was built, verified and torn down, because the cost story only works if it is torn down. What runs here now is the same application on a single hardened host on Oracle Cloud, architected for a different set of constraints. That rebuild is its own entry under Projects.
Certificates
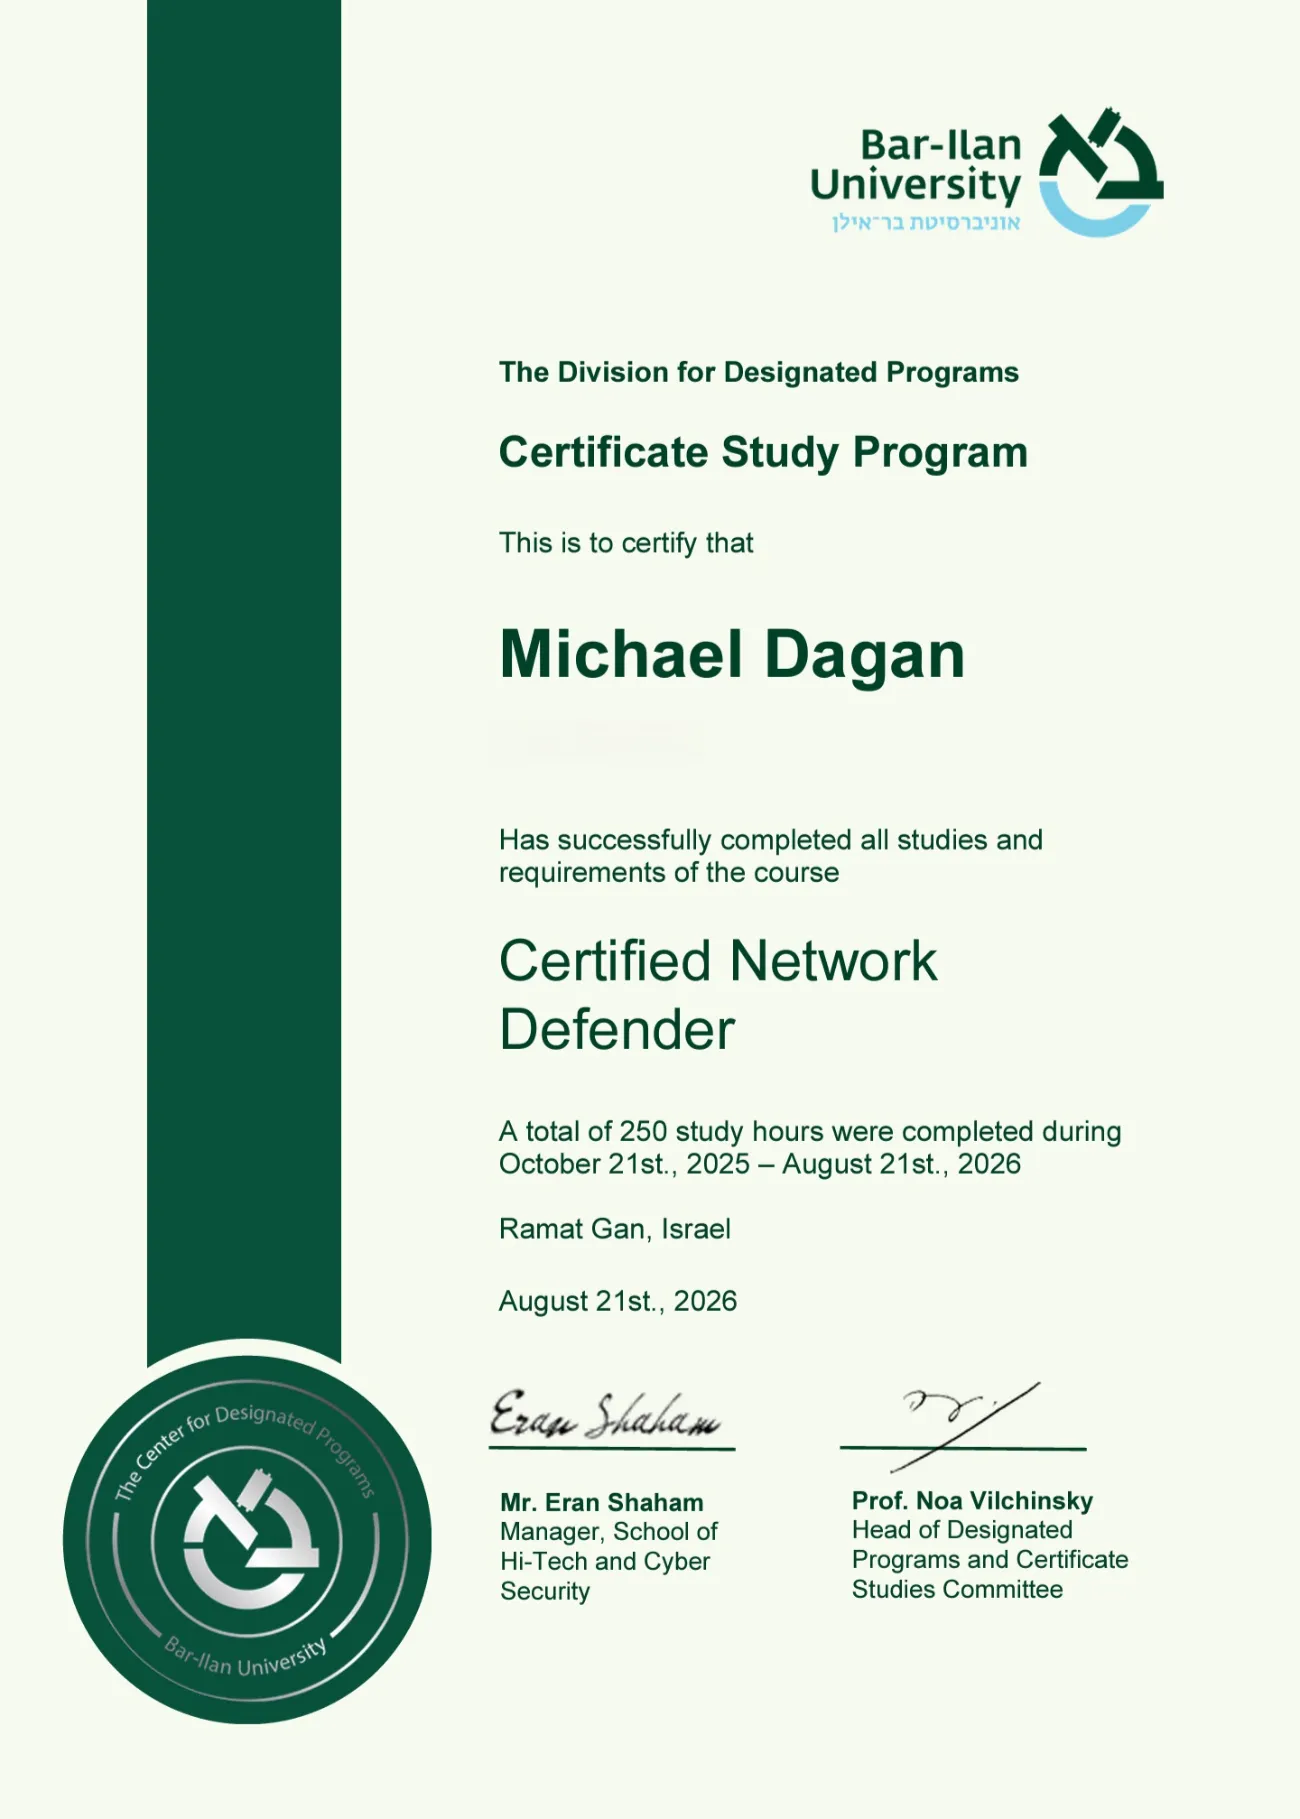 Certified Network Defender (CND 53), 250 hours - Certificate of Completion
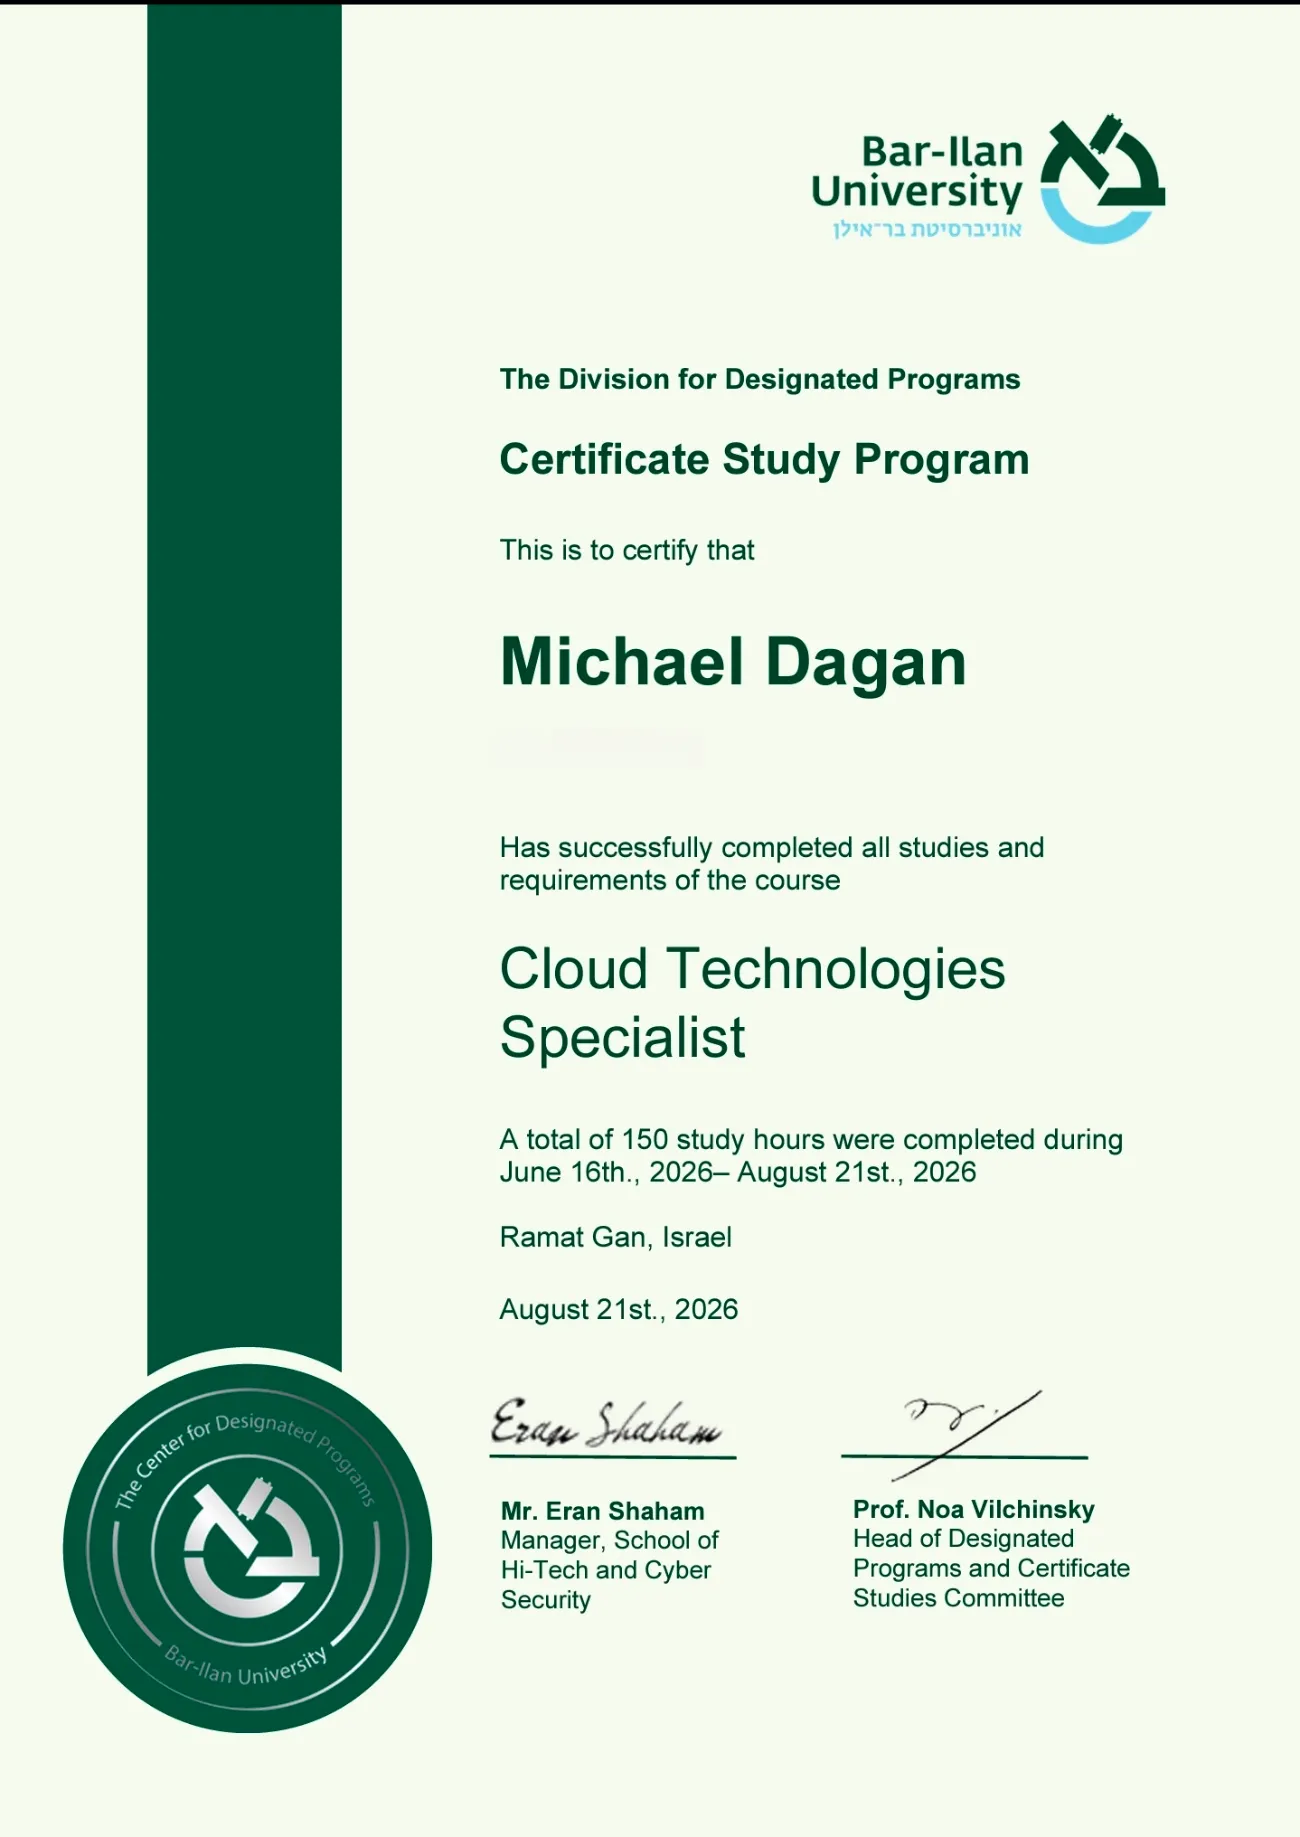 Cloud Technologies Specialist, 150 hours - Certificate of Completion
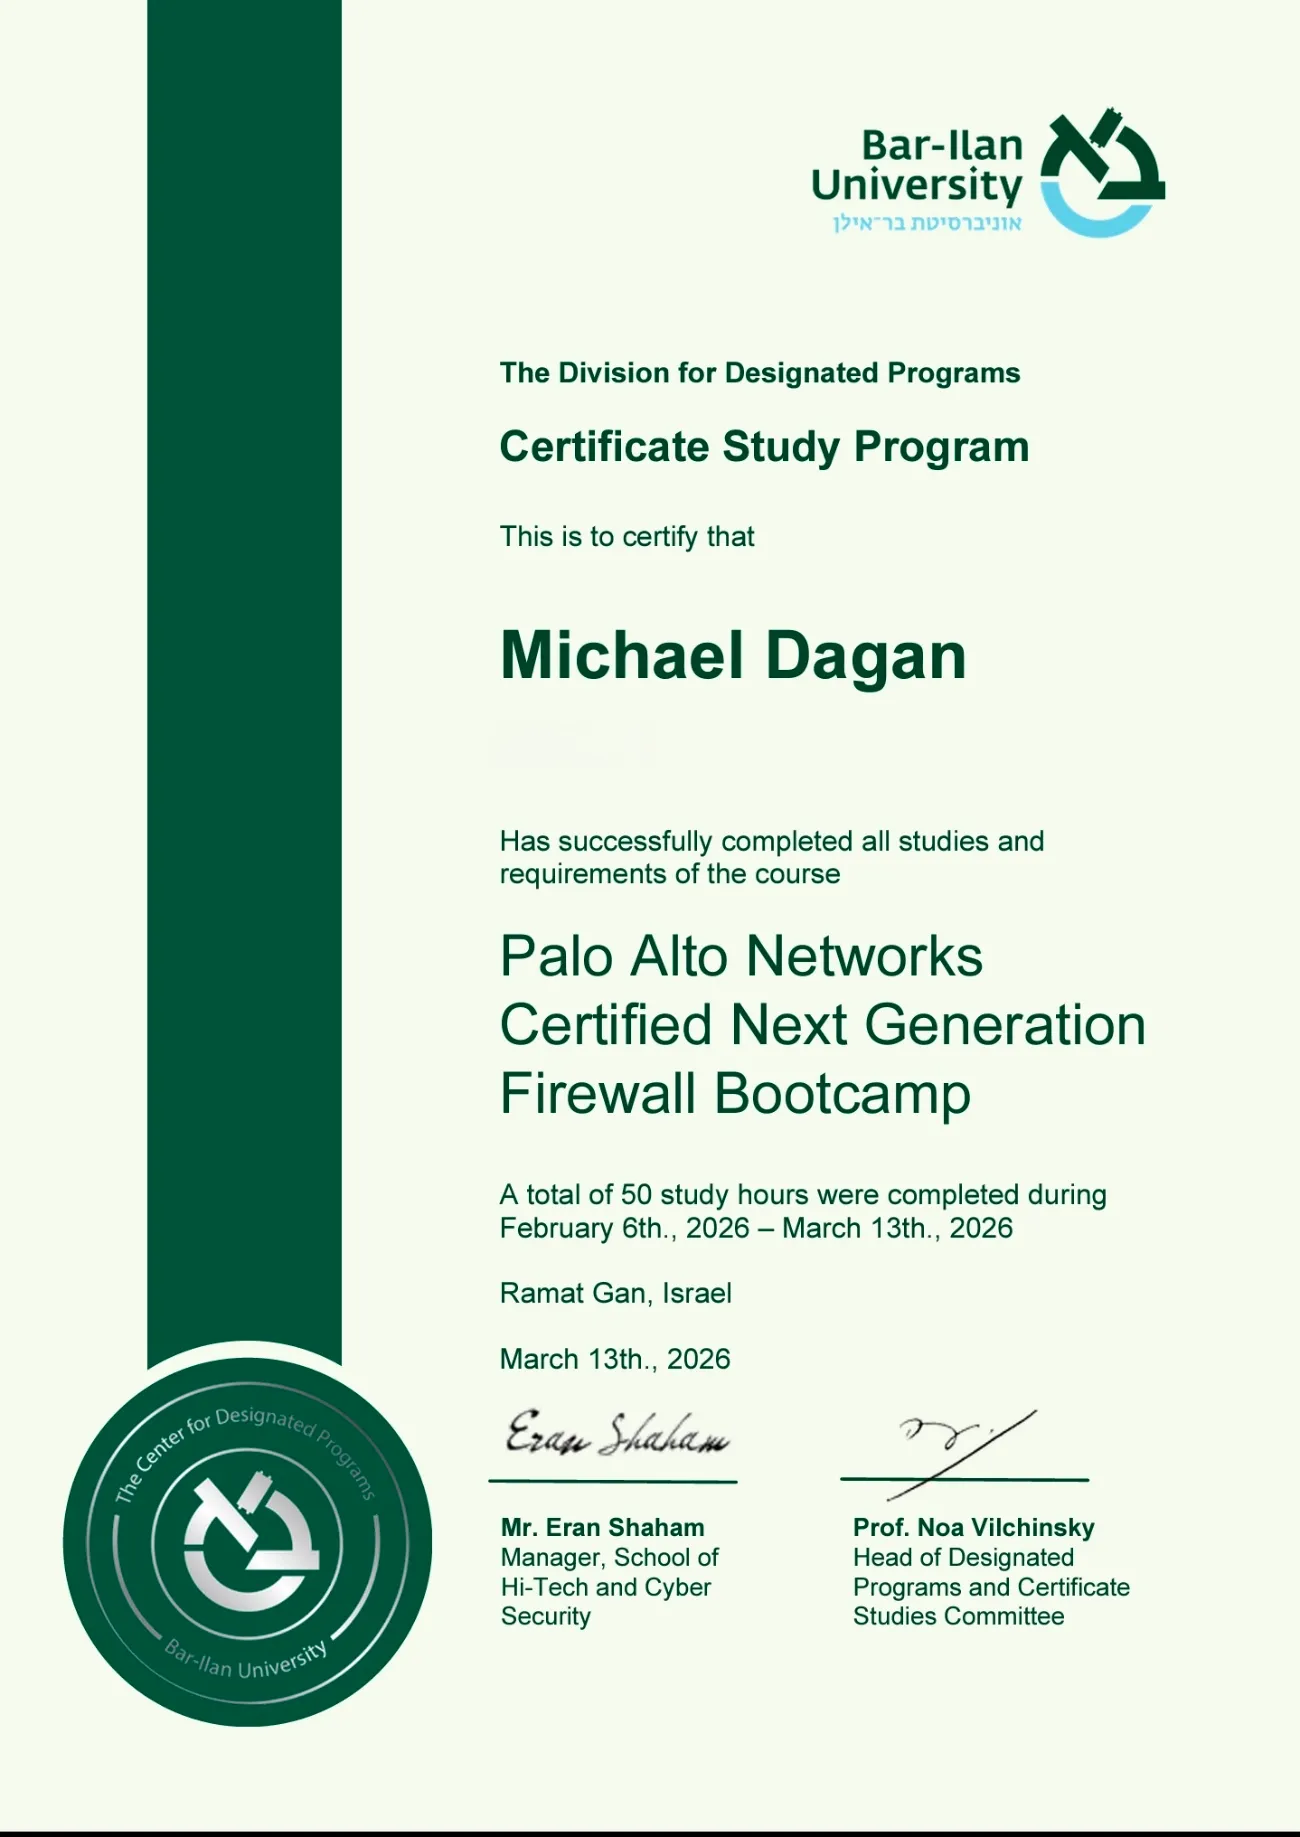 Palo Alto Networks Next Generation Firewall Bootcamp, 50 hours - Certificate of Completion
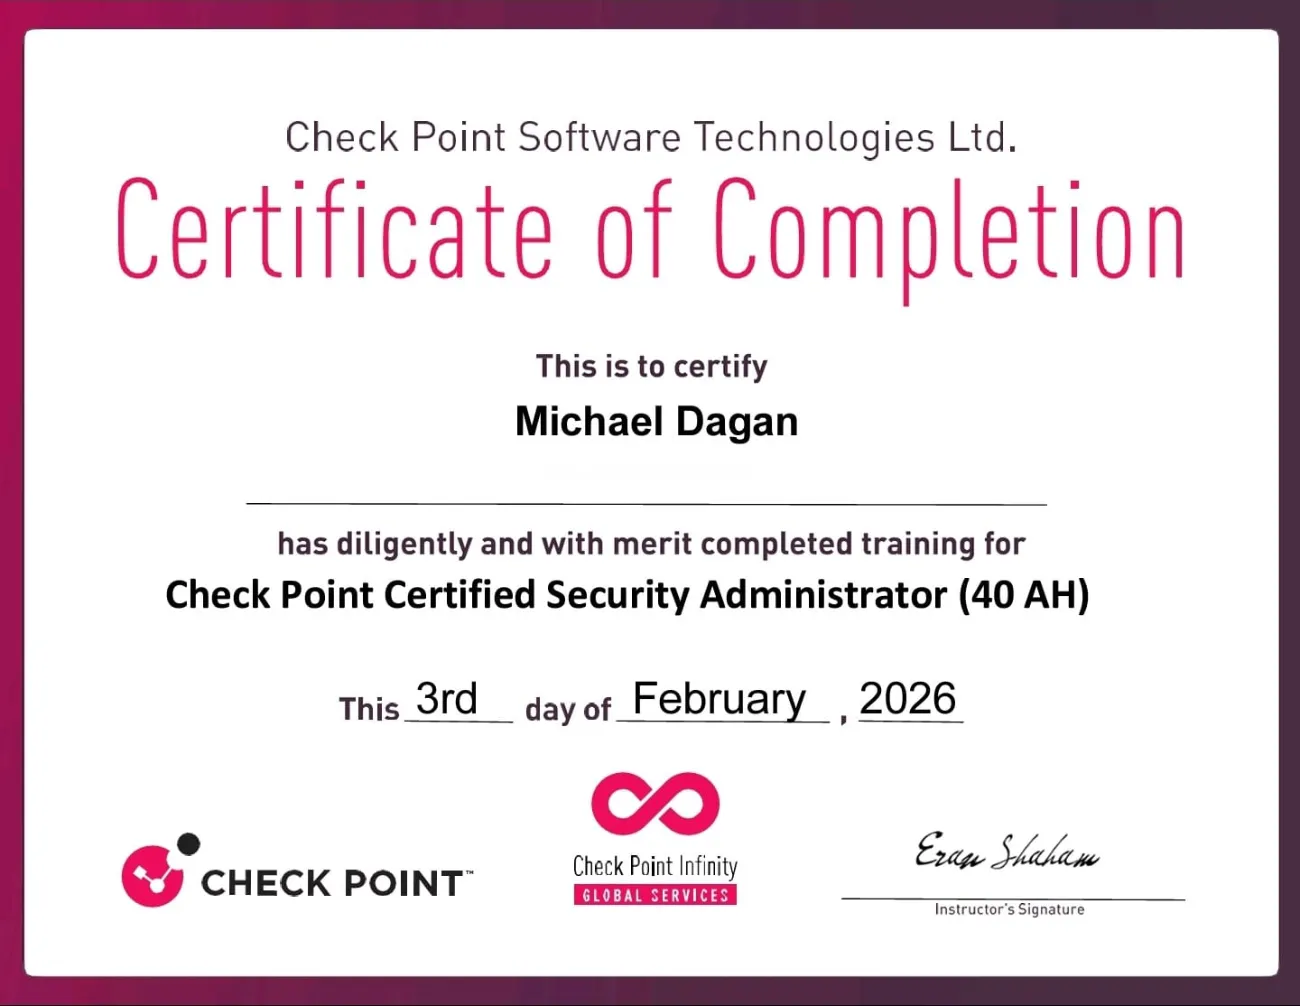 Check Point Certified Security Administrator (CCSA) Training, 40 academic hours - Certificate of Completion
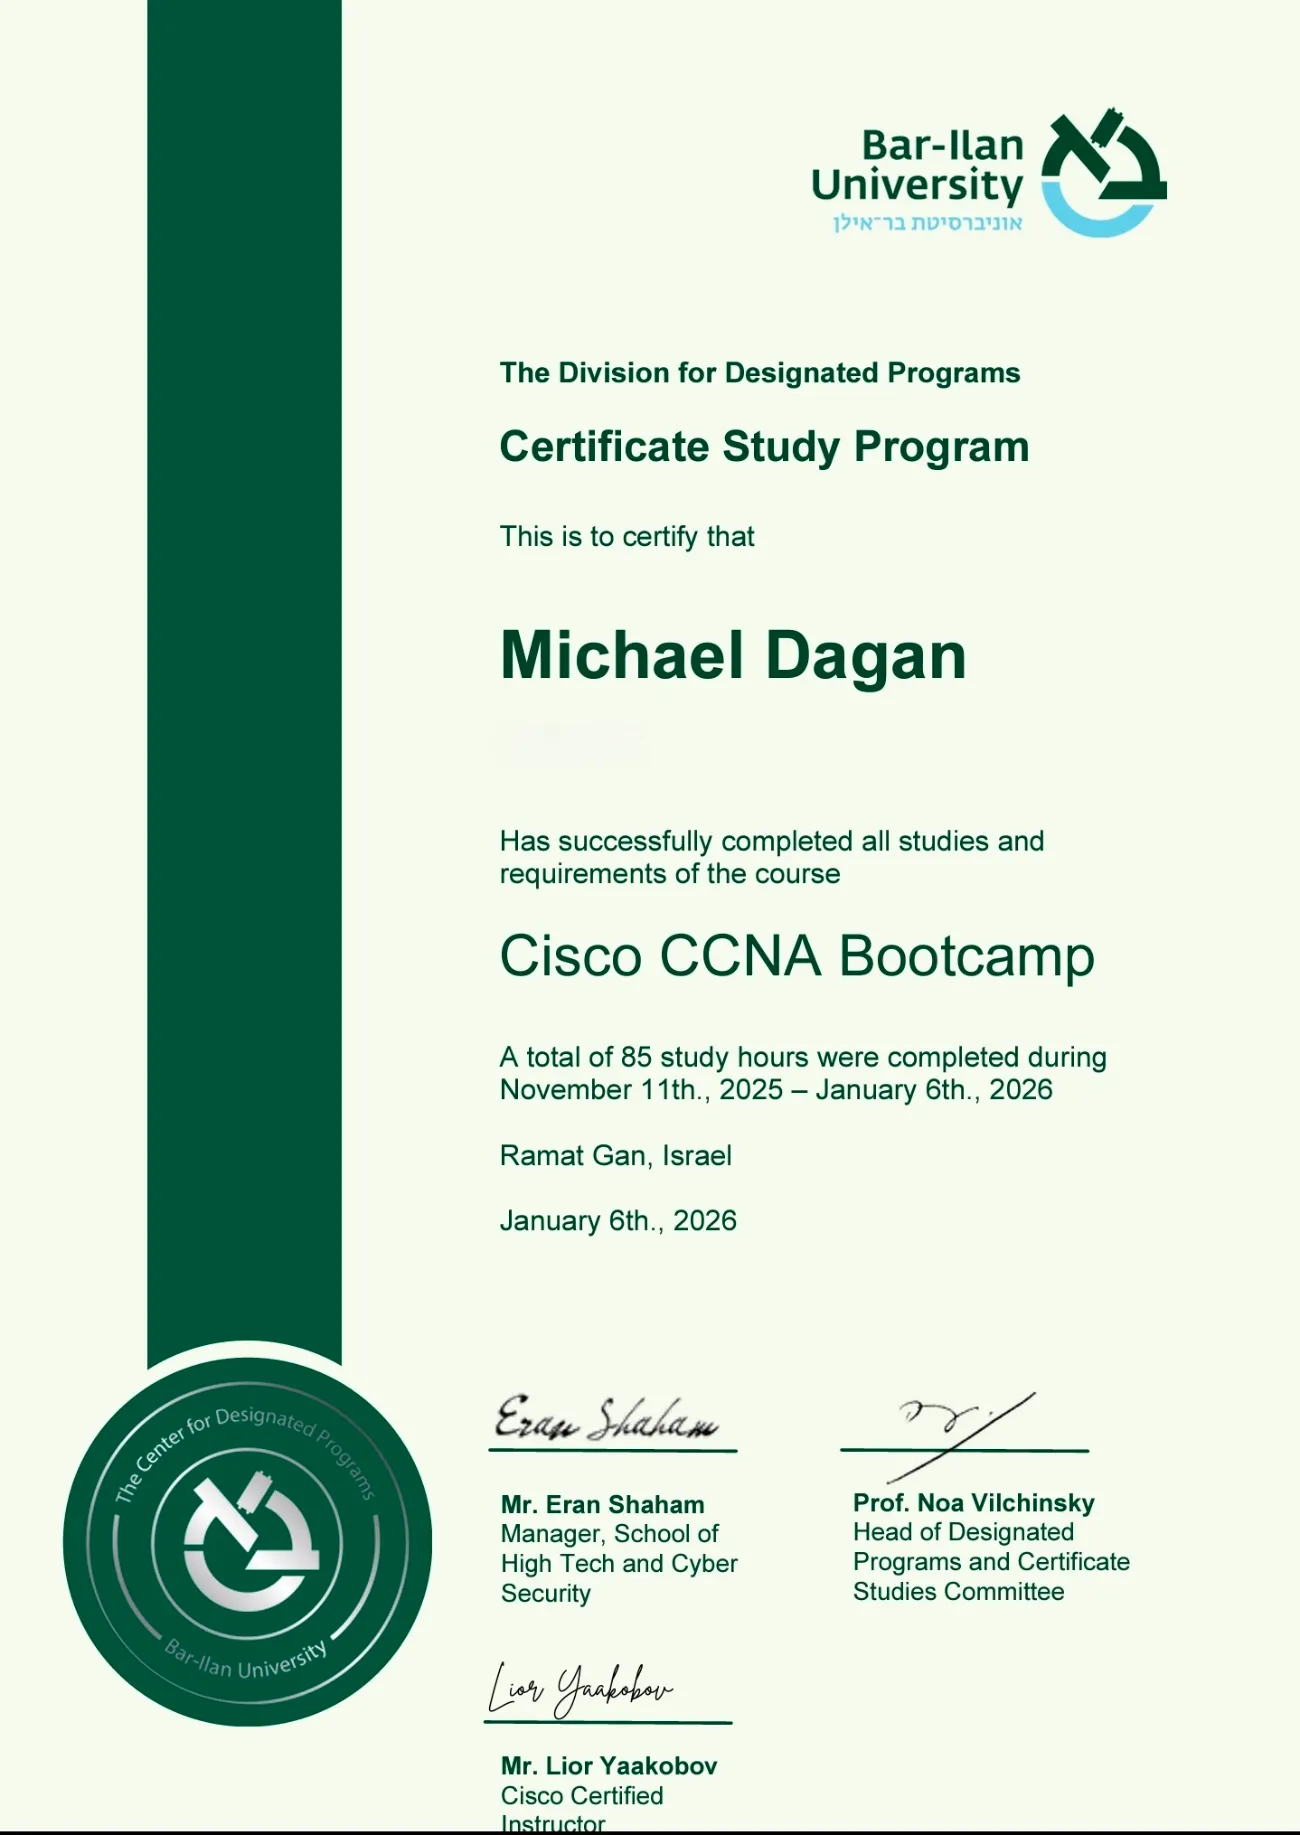 Cisco CCNA Bootcamp, 85 hours - Certificate of Completion
 AWS Academy Cloud Foundations - training badge